
作者:Jonathan Jing更新日 2026-08-03全 21 バージョン · 最新版の公開日 2026-08-03openclaw-dashboard@clawhub_jonathanjing/openclaw-dashboard
監視・アラートサーバー運用#Cron
AlphaMoatによると、2026-10時点でOpenClaw Dashboardのダウンロード数は6,665、スター数は11で、累計ダウンロード数で今回のランキング対象AIスキル10,914件中4,275位、IT運用・セキュリティでは502件中136位です。
一覧の初期表示は累計ダウンロード数順で、スター数順にも並べ替えできます。詳細ページの順位は累計ダウンロード数で計算しています。
| プラットフォーム | ダウンロード数 | スター数 | コメント |
|---|---|---|---|
| ClawHub ↗ | 5841 | 9 | - |
| SkillHub ↗ | 6665 | 11 | — |
プラットフォームごとに集計方法と集計時点が異なります。
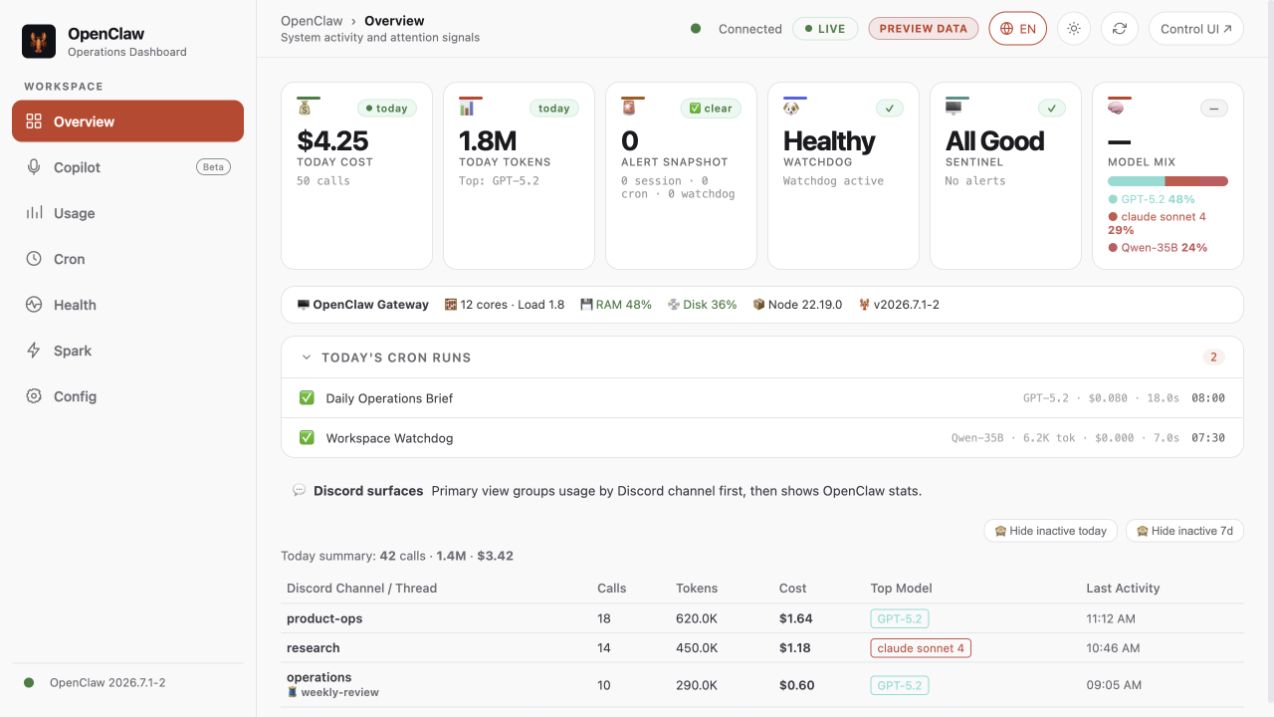
文書では、セッション、使用量とコスト、定期実行、ゲートウェイ状態、Spark作業、ローカルAPI Hubのパネルと、任意の会議Copilotを扱います。ダッシュボードはローカル運用情報を扱うため、導入前にネットワーク公開を制限し、認証トークンを保護し、機微項目とセキュリティリスクを確認してください。
資料公開日 2026-10-27
スキルのドキュメントをもとに生成した例であり、実際の実行結果ではありません。
2026-09 から集計方法を変更し、同名スキルを作者ごとに分けて集計し、全スキルを対象にしました。破線は変更前の月で、変更後のデータとは直接比較せず、変更をまたぐ増減も計算していません。
| 月 | ダウンロード数 | 前月比 | スター数 |
|---|---|---|---|
| 2026-10 | 6665 | — | 11 |
| 2026-09 | 5654 | — | 11 |
| 2026-08 | 5462 | +5.8% | 11 |
| 2026-07 | 5161 | +8.0% | 11 |
| 2026-06 | 4778 | +5.4% | 11 |
| 2026-05 | 4534 | — | 11 |
| 2026-03 | 3020 | — | 7 |
作者が公開した元のファイルをテキストのまま表示しています。AlphaMoat による編集や審査はしていません。リンクはクリックできません。コマンドは内容を確認してから実行してください。取得日 2026-10-23。
---
name: openclaw-dashboard
description: OpenClaw operations dashboard for sessions, usage and cost, cron runs, gateway health, DGX Spark work, Local API Hub, and opt-in meeting Copilot. Use when installing, operating, auditing, or extending the dashboard backend, frontend tabs, security model, or OpenClaw-aligned design.
metadata:
  openclaw:
    version: "2.0.2"
    emoji: "📊"
    homepage: https://github.com/JonathanJing/openclaw-dashboard
    requires:
bins: [node, openclaw] primaryEnv: OPENCLAW_AUTH_TOKEN
envVars:
- name: OPENCLAW_AUTH_TOKEN
required: true
description: Authentication token required before the dashboard starts.
- name: OPENCLAW_ENABLE_CONFIG_ENDPOINT
required: false
description: Opt in to redacted configuration inspection.
- name: OPENCLAW_ENABLE_COPILOT
required: false
description: Opt in to meeting audio processing.
- name: ALIBABA_CLOUD_API_KEY
required: false
description: Realtime provider credential used only when Copilot is enabled.
---
# OpenClaw Dashboard Skill
## Preview
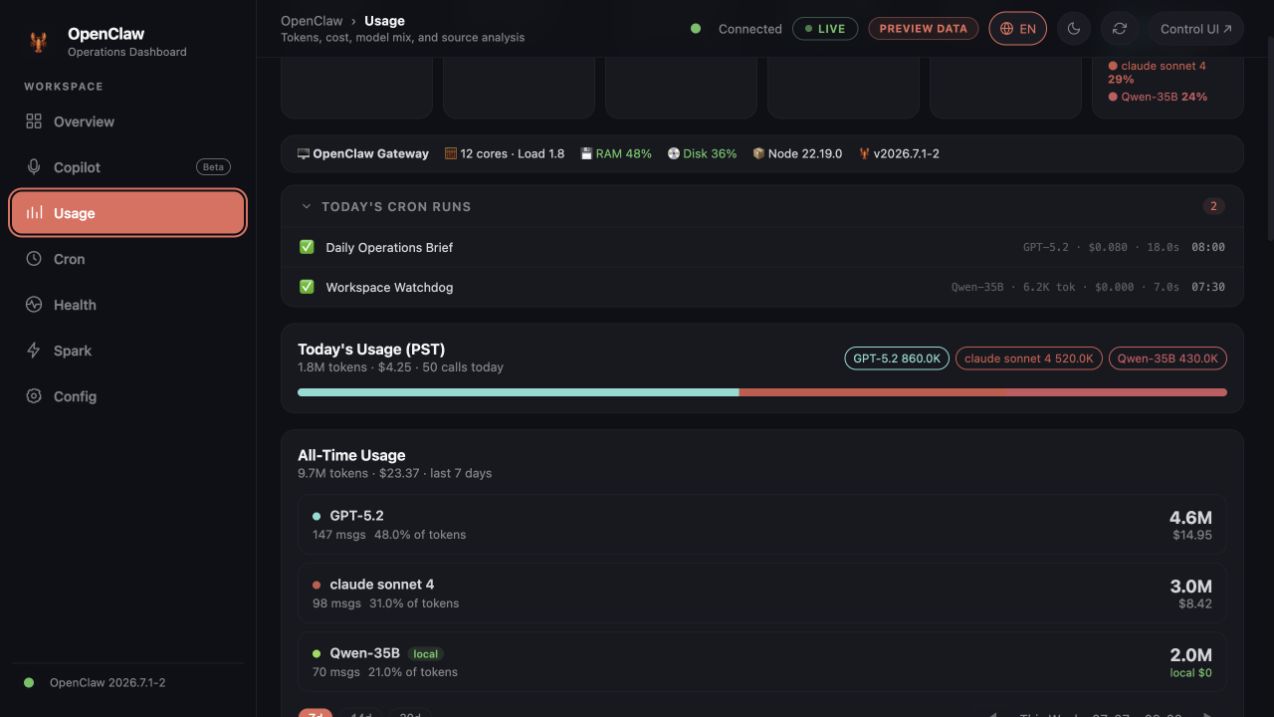
The published screenshots use deterministic `?preview=1` sample data, never local host or workspace data.
<img src="https://raw.githubusercontent.com/JonathanJing/openclaw-dashboard/71604d6831bb24b9e8340bf0d1153a9545c5a038/screenshots/mobile-v2-dark.png" alt="OpenClaw Dashboard mobile layout" width="390">
## 🛠️ Installation
### 1. Ask OpenClaw (Recommended)
Tell OpenClaw: *"Install the openclaw-dashboard skill."* The agent will handle the installation and configuration automatically.
### 2. Manual Installation (CLI)
```bash
openclaw skills install @jonathanjing/openclaw-dashboard
```
## Mission
Keep this repository public-safe and easy to run. Prioritize:
1. Secret sanitization
2. Minimal setup steps
3. Stable API/UI behavior
## Architecture (v2.0)
The dashboard uses a **modular backend + tab-based frontend** architecture.
**Backend entry point:** `backend/server.js`
**Business logic:** `backend/providers/` — one file per data domain
**Frontend:** `frontend/tabs/` + `frontend/shared/` — one JS file per tab
**Runtime data:** stored in `~/.openclaw/dashboard/` (outside skill dir, not Git-tracked)
### Provider map
| Provider | Routes | Responsibility |
|---|---|---|
| `sessions.js` | `/ops/sessions`, `/api/sessions` | Session stats + model |
| `ledger.js` | `/ops/ledger/*`, `/api/cost/*` | SQLite token/cost data |
| `cron.js` | `/ops/cron`, `/ops/cron-costs`, `/cron/today` | Cron jobs + run history + cost breakdown |
| `watchdog.js` | `/ops/watchdog` | Watchdog state + timeline |
| `spark.js` | `/ops/dgx-status`, `/api/spark/*` | DGX Spark inference node |
| `system.js` | `/ops/system` | Host metrics (CPU/RAM/disk) |
| `local-api-hub.js` | `/ops/local-api-hub/*` | Unified local control-plane status |
| `spark-tasks.js` | `/api/spark/tasks/*` | DGX task history and PR Hunter output |
| `copilot.js` | `/api/copilot/status`, `/api/copilot/ws` | Opt-in realtime transcript/RAG/insights |
| `ground-truth.js` | `/api/ground-truth/*`, `/ops/models` | Model registry + colors |
| `tasks.js` | `/tasks`, `/tasks/:id`, `/logs` | Read-only task/history views |
| `config.js` | `/ops/config`, `/files`, `/skills` | Read-only config, file, and skill views |
| `ops-legacy.js` | `/ops/channels`, `/ops/alltime`, `/ops/audit`, `/memory` | Read-only compatibility views |
### Frontend tab map
| Tab | File | Key functions |
|---|---|---|
| Overview | `tabs/overview.js` | `loadSessions()`, `loadTasks()` |
| Cost | `tabs/cost.js` | `loadOpsChannels()`, `loadOpsAlltime()` |
| Cron | `tabs/cron.js` | `loadCronEnhanced()`, `loadCronCosts()`, `loadCronRuns()` |
| Health | `tabs/health.js` | `renderAgentMonitor()`, `loadSystemInfo()`, `renderWatchdogStatus()` |
| Spark | `tabs/spark-monitor.js` | `loadSparkMonitor()`, task history, GPU activity |
| Copilot | `tabs/copilot.js` | capability check, microphone stream, transcript/RAG/insights |
| Config | `tabs/config.js` | `loadConfig()`, `loadSkills()`, `loadFileList()` |
| Shared | `shared/api.js` | Auth, `apiFetch()`, watchdog renderers, toast, markdown |
| Shared | `shared/ui-utils.js` | `timeSince()`, task state |
| Shared | `shared/boot.js` | Init, week nav, chart renderers, confirm dialog |
## Apply when
Use this skill for:
- Dashboard feature requests (sessions, cost, cron, watchdog, operations)
- Backend route additions/fixes in `backend/providers/`
- Frontend behavior updates in `frontend/tabs/` or `frontend/shared/`
- README, setup, and environment simplification
- Public release checks for accidental sensitive data
## Key rules for agents editing this codebase
1. **No duplicate function definitions** across `api.js` and `ui-utils.js`. Shared utilities belong in `api.js` (loaded first). `ui-utils.js` only holds `timeSince()` and task state.
2. **Cross-tab function calls are implicit** — JS shares the same `window` scope. Keep shared helpers in `shared/` files.
3. **Runtime data goes to `~/.openclaw/dashboard/`**, not skill root. Path is set in `backend/lib/config.js` via `OPENCLAW_DASHBOARD_TASKS` env or default.
4. **`/ops/models` returns `{ registry: {...object...}, colors, displayNames, models }`** — `registry` must be an object keyed by alias, not an array.
5. **`/ops/cron-costs` returns `{ summary, jobs, dailyTrend, review, rows }`** — all five keys required for Cron tab to render correctly.
6. **`hideStale` query param** on `/ops/sessions` filters sessions with no activity for 7+ days.
7. **Frontend API calls are same-origin**. Never reintroduce a hardcoded dashboard/gateway port list.
8. **Copilot is opt-in**. Require `OPENCLAW_ENABLE_COPILOT=1`, an API key, authenticated WebSocket upgrade, and safe dependency failure states.
9. **Parse request URLs against a fixed internal base**. Never build a URL from the request `Host` header.
10. **Treat query-token login as a compatibility handoff only**. Set the cookie and redirect before serving HTML; never accept query tokens on API routes.
11. **Parse cookies per fragment**. Split on the first `=`, catch percent-decoding errors, and encode cookie values when setting them.
12. **Keep the shipped dashboard read-only**. Do not add task/file mutations, restart/doctor actions, model changes, package updates, backup/restore, or legacy proxying.
13. **Scope Copilot Redis events by meeting ID**. Permit unscoped legacy channels only for the first active meeting.
14. **Track the launcher and test harness**. Keep `start.sh` and `scripts/test-dashboard.js` in both Git and `package.json#files`.
15. **Use theme tokens in canvas rendering**. Never hardcode light-only chart text or borders.
## OpenClaw design alignment
- Reuse the current Control UI tokens: Inter/system typography, layered neutral surfaces, thin borders, 10–14px radii, red primary accent, semantic green/yellow/red/blue.
- Keep the desktop shell as left navigation + sticky topbar; use bottom navigation on narrow screens.
- Prefer flat cards and strong information hierarchy over gradients, glow, or decorative motion.
- Support dark and light modes, visible focus states, reduced motion, and responsive layouts.
- Keep IDs and `data-tab` contracts stable when changing navigation or visual structure.
## Public-safety guardrails
- Never hardcode tokens, API keys, cookies, or host-specific secrets.
- Require `OPENCLAW_AUTH_TOKEN`; do not start the dashboard without authentication.
- Never commit machine-specific absolute paths.
- Prefer `process.env.*` and safe defaults based on `HOME`.
- Keep examples as placeholders (`your_token_here`, `/path/to/...`).
- If uncertain, redact first and ask the user before exposing details.
- Keep sensitive behaviors opt-in (do not silently load local secret files).
## Runtime access declaration
The bundled server can access local OpenClaw files for dashboard views:
- Sessions, cron runs, watchdog state under `~/.openclaw/...`
- Local workspace files under `OPENCLAW_WORKSPACE`
- Task data in `~/.openclaw/dashboard/tasks.json`
- Task attachments in `~/.openclaw/dashboard/attachments/`
High-sensitivity features are disabled by default and require explicit env flags:
- `OPENCLAW_ENABLE_CONFIG_ENDPOINT=1` to expose `/ops/config`
- `OPENCLAW_ENABLE_COPILOT=1` plus `ALIBABA_CLOUD_API_KEY` to enable meeting Copilot
Network security:
- CORS restricted to loopback by default.
- Auth via HttpOnly cookie (`ds`) or `Authorization: Bearer` header.
- Set `DASHBOARD_COOKIE_SECURE=1` only when the dashboard origin uses HTTPS.
- Set `OPENCLAW_CONTROL_UI_URL` to the complete runtime URL when Gateway TLS or `gateway.controlUi.basePath` is enabled.
- Set `DASHBOARD_CORS_ORIGINS` (comma-separated) for external origins.
## Default implementation workflow
1. Identify which provider or tab file owns the feature.
2. Implement the smallest change that preserves behavior.
3. Check: does any other tab/shared file also define the same function? If yes, deduplicate.
4. Run a sensitive-string scan before finalizing.
5. Run `npm test`, `git diff --check`, and `npm pack --dry-run --json`.
6. Ensure docs match the actual runtime defaults.
## Sensitive-data checks
Before final response, scan for:
- `token=`, `OPENCLAW_AUTH_TOKEN`, `OPENCLAW_HOOK_TOKEN`
- `API_KEY`, `SECRET`, `PASSWORD`, `COOKIE`
- absolute paths like `/Users/`, `C:\\`, machine names, personal emails
If found: replace with env-based values or placeholders, and mention what was sanitized.
## Files to touch most often
- `backend/providers/*.js` — server behavior and API routes
- `frontend/tabs/*.js` — tab-specific UI logic
- `frontend/shared/api.js` — auth, fetch, shared renderers
- `backend/lib/config.js` — path and env configuration
- `README.md` — quick start and operator docs
- `env.example.txt` — ClawHub-compatible public-safe environment template
- `env.example` — compatibility mirror for Git/npm workflows
钟馗.Skill——会更新漏洞库的安全审查专家。直来直去、快刀斩乱麻,三层审查(静态审计/行为模拟/供应链溯源)覆盖12类风险,输出结构化安全裁定(✅干净/⚠️可疑/🚫恶意)。Use when 用户说"审查这个Skill"、"安全检查"、"钟馗看下"、"审一下"、"查一下这个skill"、安装Skill前的安全评估、或需要审计SKILL.md的恶意载荷。
使う前にスキルパッケージの安全性を調べ、結果に応じて導入を止めるスキルです。
OpenClaw に OpenRouter の無料モデルとフォールバック連鎖を設定するツールです。
Parse, search, and analyze application logs across formats. Use when debugging from log files, setting up structured logging, analyzing error patterns, correlating events across services, parsing stack traces, or monitoring log output in real time.
Security checks for installing skills, packages, or plugins. Use BEFORE any npm install, openclaw plugins install, clawhub install, or similar install...
网络安全与SRC漏洞掘金实战技能。融合「系统学习路径」与「SRC实战掘金」双模式: ①学习模式=法律→基础→工具→靶场→攻防→就业全流程; ②实战模式=直接指导在腾讯TSRC、阿里ASRC、百度BSRC等平台挖掘高价值漏洞变现。 当用户提出以下问题时触发: "我想学网络安全怎么入门""SRC漏洞怎么挖能赚钱""渗透测试需要学什么" "Web安全漏洞原理是什么""怎么准备CTF比赛""护网面试会问什么" "云安全怎么学""挖漏洞赚钱的方法""端口扫描脚本怎么写" "SQL注入怎么检测""子域名怎么枚举""XSS漏洞怎么找" "靶场怎么搭建""Kali Linux怎么用""Metasploit怎么入门" "等保测评是什么""代码审计怎么做""内网渗透怎么学" "信息泄露漏洞怎么挖""越权漏洞怎么测试""逻辑漏洞挖掘技巧" "简历怎么写才能进安全公司""安全行业面试题有哪些" "Burp Suite怎么用""DVWA怎么安装""Pikachu靶场搭建" "Vulhub漏洞复现""网络安全法有什么规定""CTF夺旗赛怎么参加" "AWD比赛是什么""应急响应怎么做""攻击溯源怎么搞" "数据安全怎么保障""公有云安全怎么防护""私有云攻防怎么做" "云原生安全是什么"。
Unified Web penetration testing and SRC vulnerability hunting Skill. Model-driven threat modeling (12 dimensions), JSON 字段规范 state persistence, SRC/补天 compliant reporting with confirmed gate (3-layer determination). Use when user asks for authorized penetration testing, vulnerability assessment, SRC hunting (补天/Butian/vendor SRC/CNVD/众测), bug bounty, security evaluation with explicit target URL, or wants operational Recon→PoC→Report workflow. Do NOT use for CTF challenges, unauthorized testing, mobile app testing, infrastructure scanning, or social engineering.
Security-first skill vetting for AI agents. Use before installing any skill from ClawdHub, GitHub, or other sources. Checks for red flags, permission scope, and suspicious patterns.
データ月:2026-10 · ダウンロード数とスター数は公開スキルレジストリ(ClawHub、SkillHub)から月単位で集計しています。詳しくはデータの方法論をご覧ください。